ArkSentry
Pentest report
app.company.com
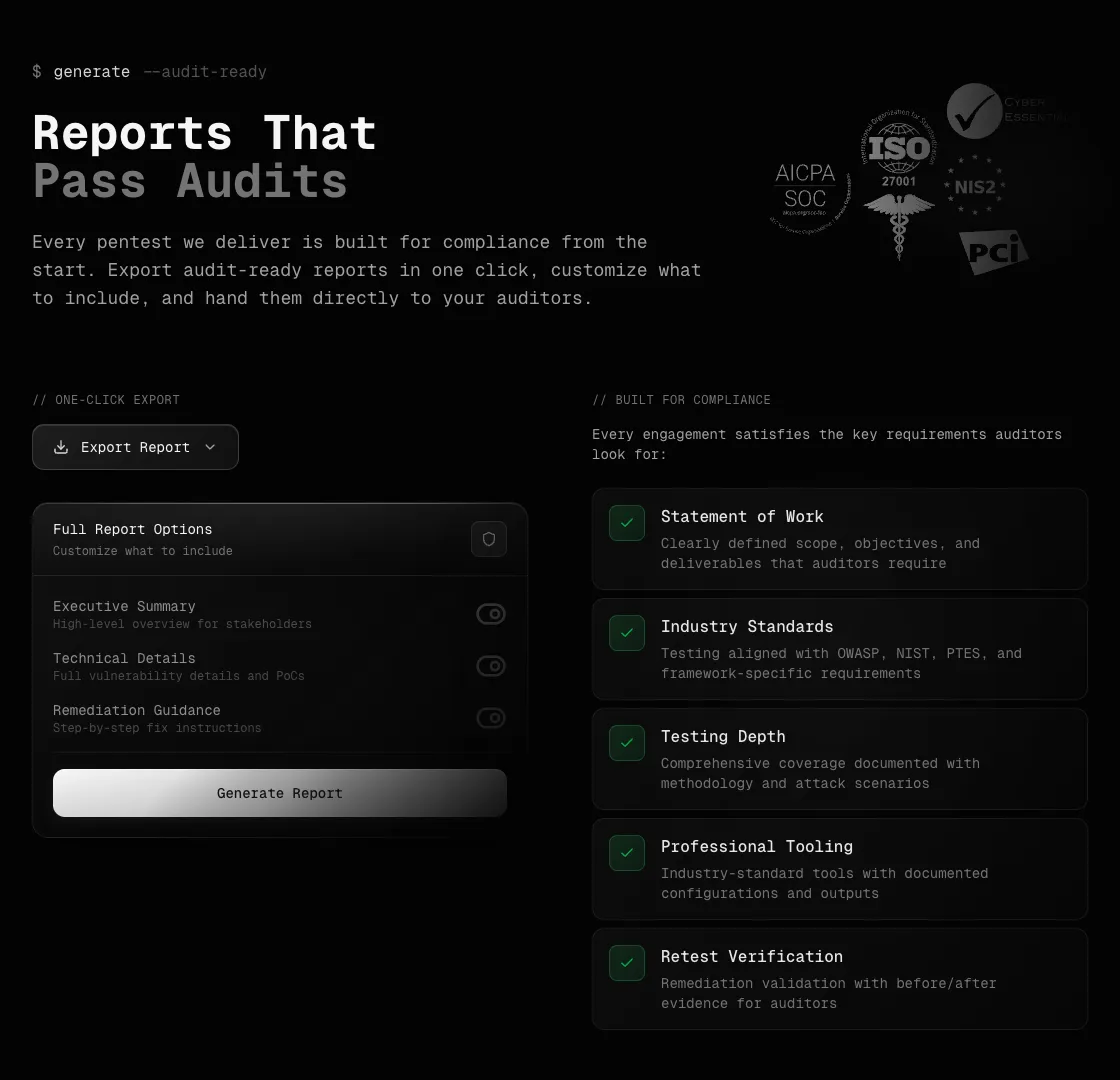
✓ Executive summary
✓ Technical details
✓ Remediation guidance
CVSS severity distribution
Critical3
High5
Medium8
Low8
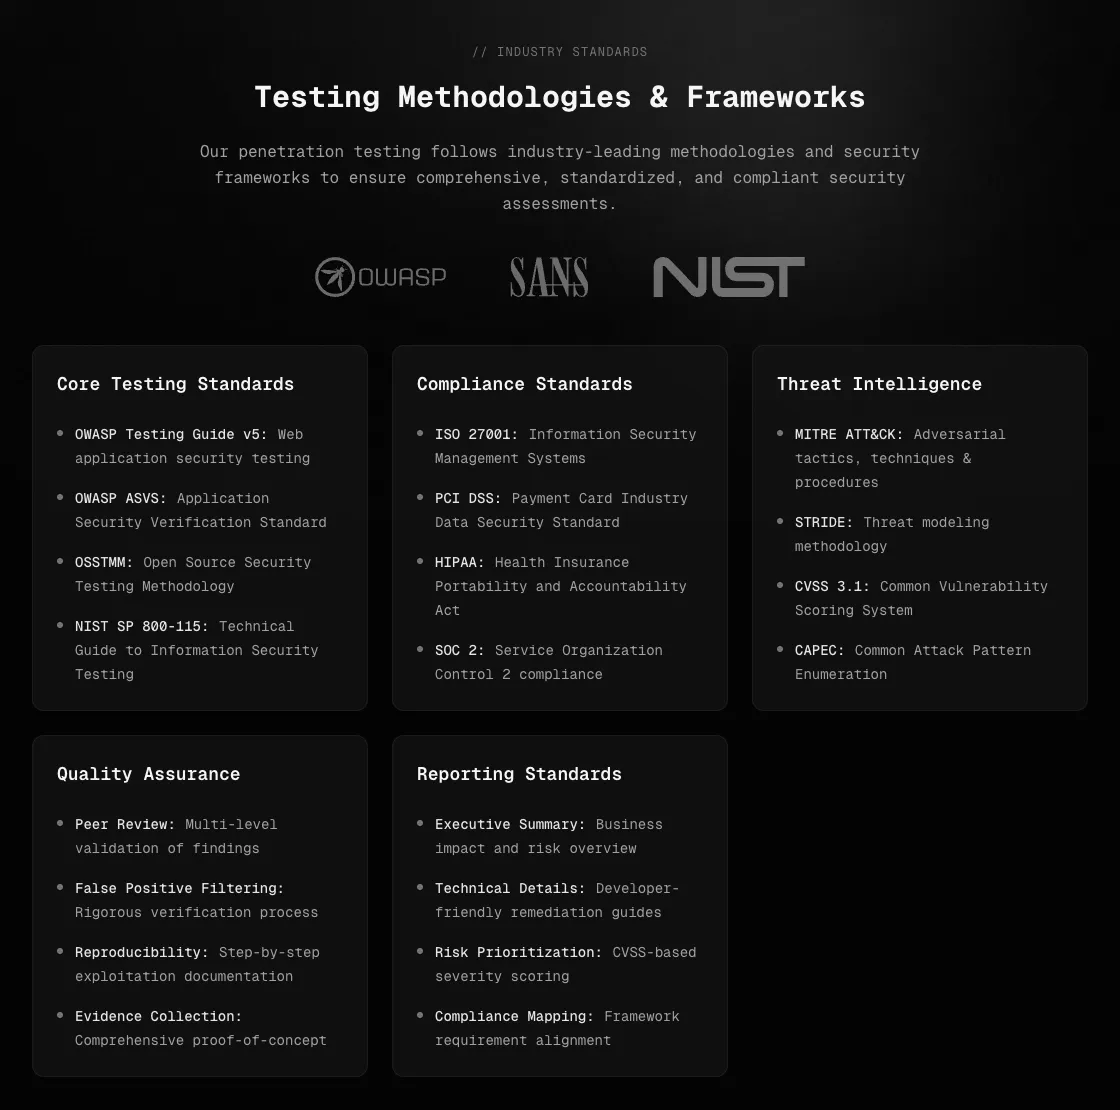
✓ SOC 2✓ ISO 27001✓ PCI DSS✓ HIPAA✓ NIST
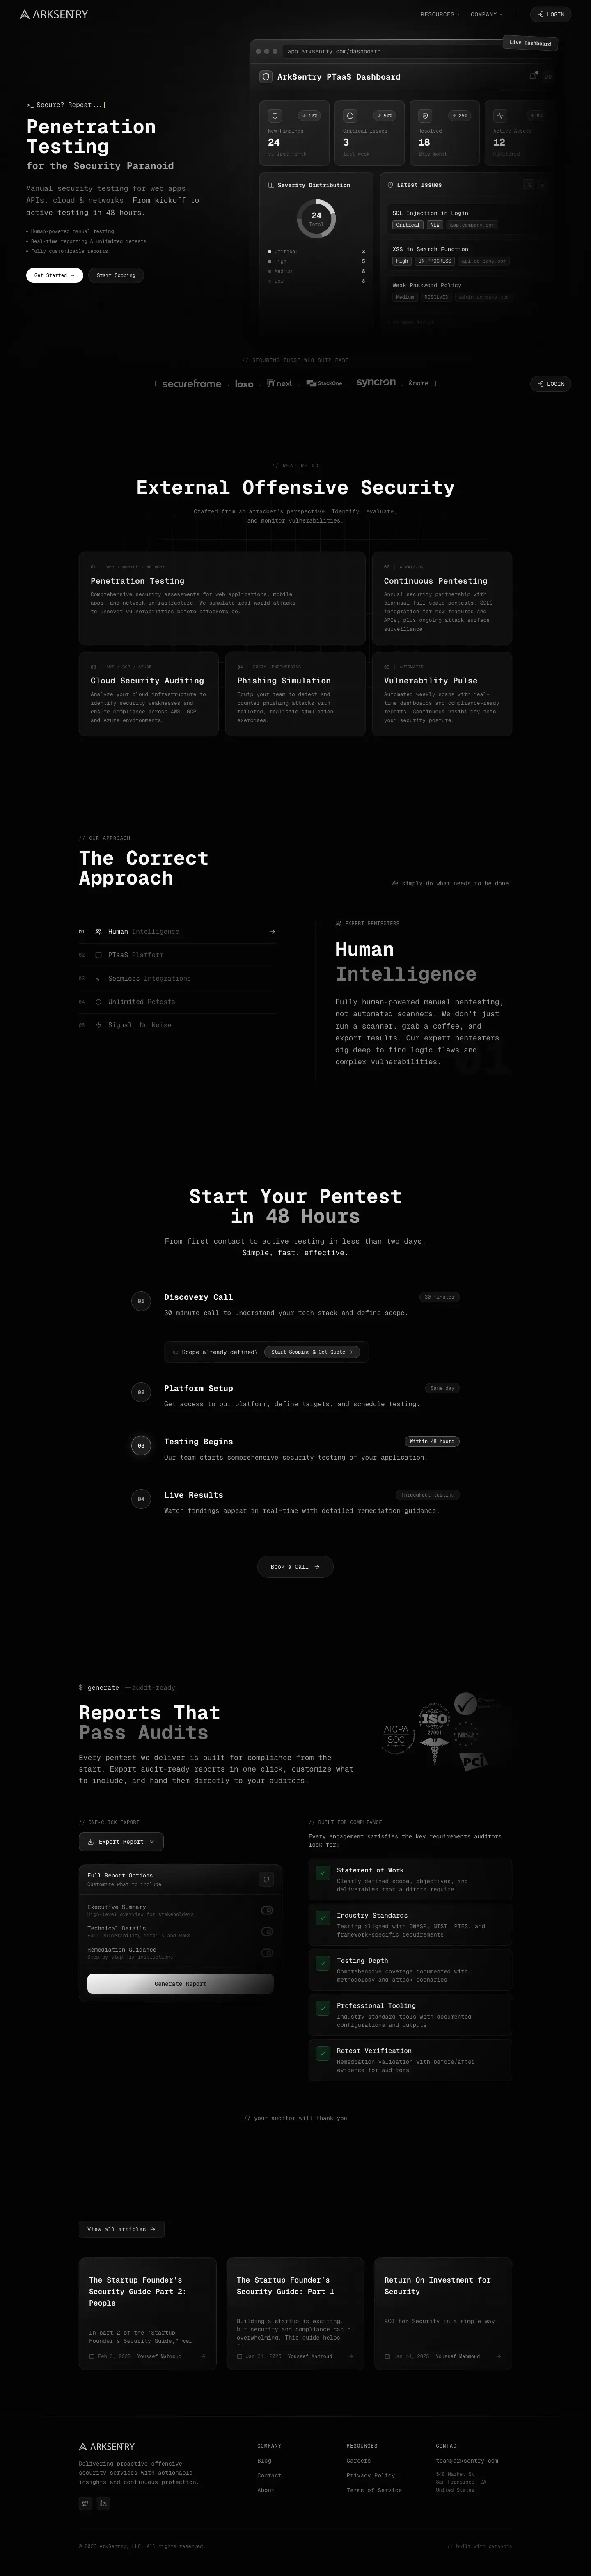
Penetration Testing for the Security Paranoid
Penetration Testing as a Service for modern teams — human-powered testing for web apps, APIs, cloud, and networks, with live findings, unlimited retests, and audit-ready reports.
$ arksentry scope --target app.company.com
[✓] 14 endpoints discovered
[!] CRITICAL SQL injection in /login
[✓] report ready — audit-ready
Human-powered testing, online in 48 hours.
>_ active assessment
From the first asset to the final retest, every signal stays visible.
Compact assessment map — final tested state
Map every exposed asset, dependency and trust boundary before testing begins.
Manual testing uncovers business-logic flaws automated scanners routinely miss.
Every verified finding lands in the dashboard the moment it is discovered.
SQL Injection in Login
Critical
XSS in Search Function
High
Weak Password Policy
Medium
Patch with clear evidence, then validate the fix with unlimited retests.
SQL Injection in Login
Resolved
XSS in Search Function
Resolved
Weak Password Policy
Resolved
$ initiate --fast
No weeks of procurement limbo. Scope today, start testing within two days, and watch verified results arrive live.
Align on scope, risk and testing goals.
Add assets, owners and secure access.
A human pentester starts the active assessment.
Findings, evidence and fixes update in real time.
$ generate --audit-ready
Turn verified findings into evidence your engineers, executives and auditors can act on.
Interactive report-builder simulation
>_ production
A security-first marketing experience that explains a complex service without slowing down the decision.

// shipped
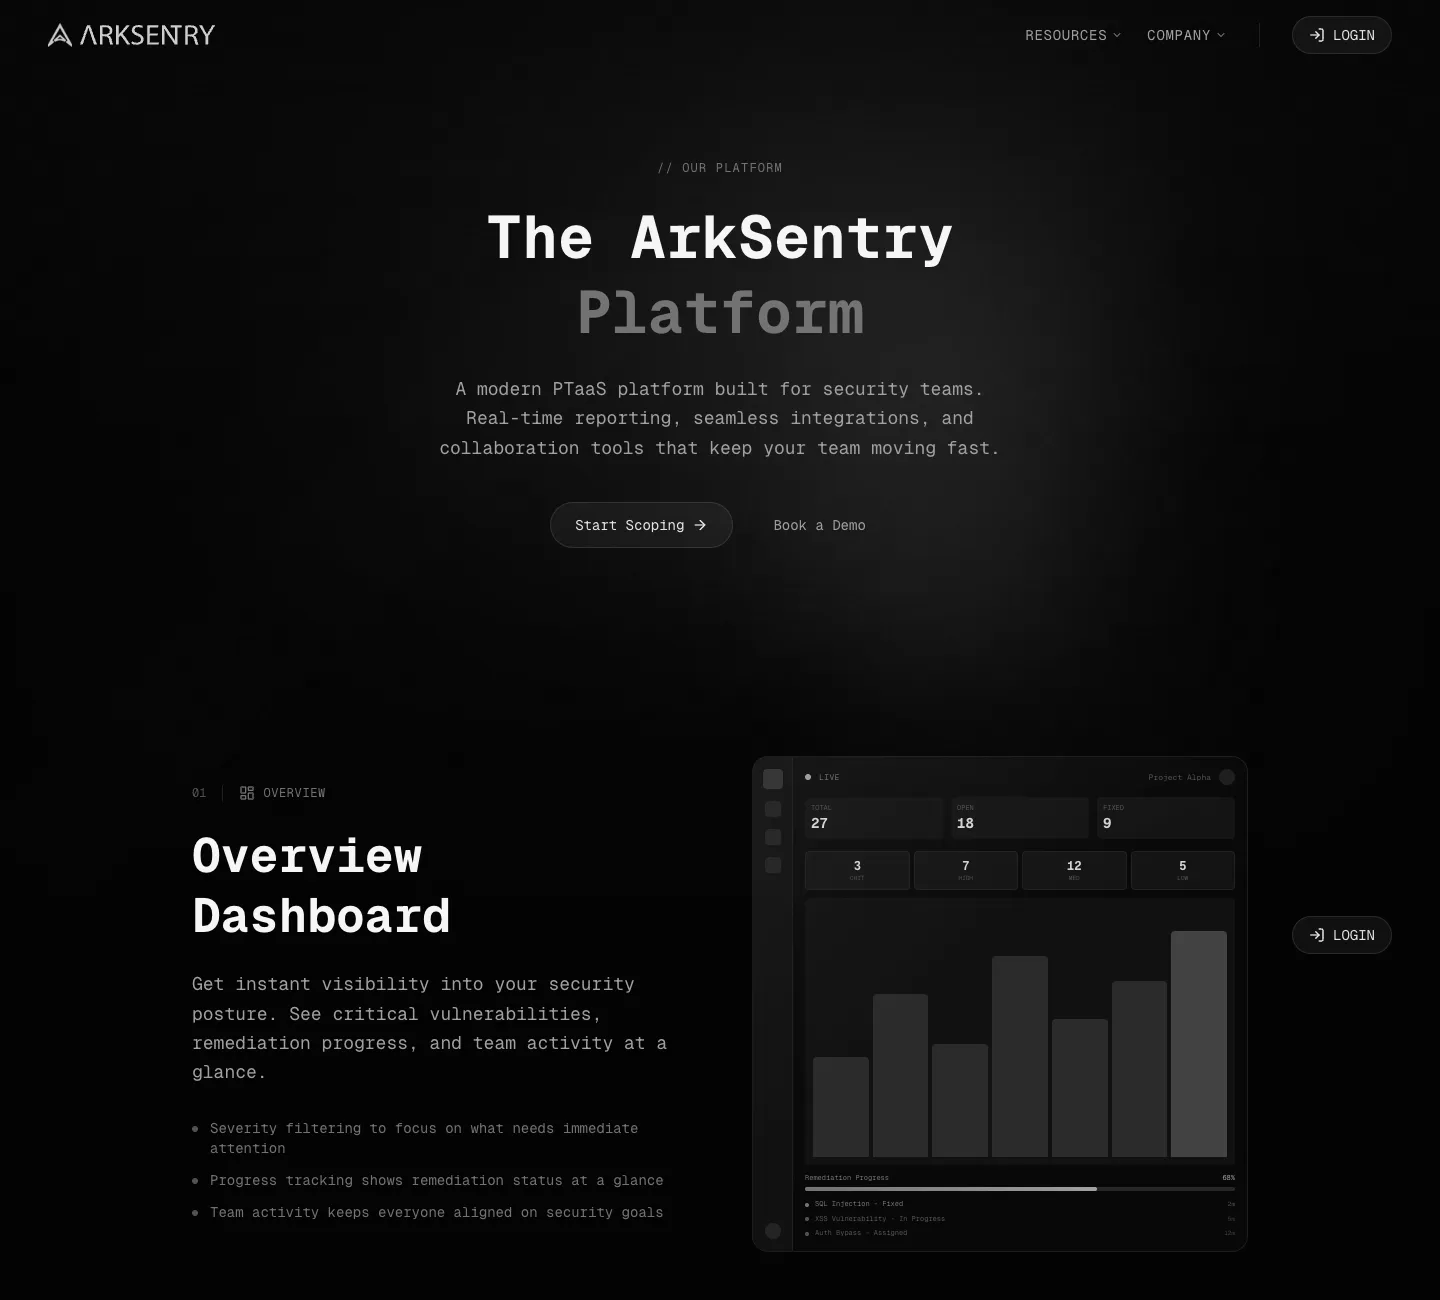
Enum Grow designed and built the marketing site and PTaaS dashboard UI with Next.js, TypeScript and Tailwind CSS.
Kickoff to active testing
Security services
Compliance frameworks
Bounce rate after redesign
Project brief
ArkSentry sells manual penetration testing to technical buyers who distrust marketing. We designed and built the marketing site and the product interface, so the offer reads clearly and the findings dashboard feels like a real security tool.
We worked with the founders to define who buys, what they compare against, and which compliance frameworks they need to see, then structured the site around those questions.
A dark, precise visual language for a security audience, plus product screens for findings, severity, and report export that were reviewed with the testing team.
Next.js and TypeScript on the front end, connected to the client's C# services and live updates, so findings appear as testers log them.
We tested performance and accessibility on every page, and checked the product views with real finding data at different severities and volumes.
We launched the new site with redirects from the old URLs, so existing search traffic was kept.
We continue to support new pages and product views as the service grows.
Speaks to technical buyers
Plain language, compliance mapping, and no vague claims.
Site and product in one style
Marketing and dashboard feel like the same company.
Works with the client's backend
We integrated with their existing C# services rather than replacing them.
A practical guide to website starting prices in Egypt, what changes the scope, what is included, and how to compare written quotes.
Read article
Most bilingual sites treat Arabic as an afterthought. These are the technical and design rules that make both languages feel native — and rank.
Read articleNext project
View all projects
Media & Production
A cinematic web experience for a film production company — cutting-edge visuals and storytelling that match the studio's creative ambition.
Tell us what you need. You get a clear scope and a written quote within 24 hours.